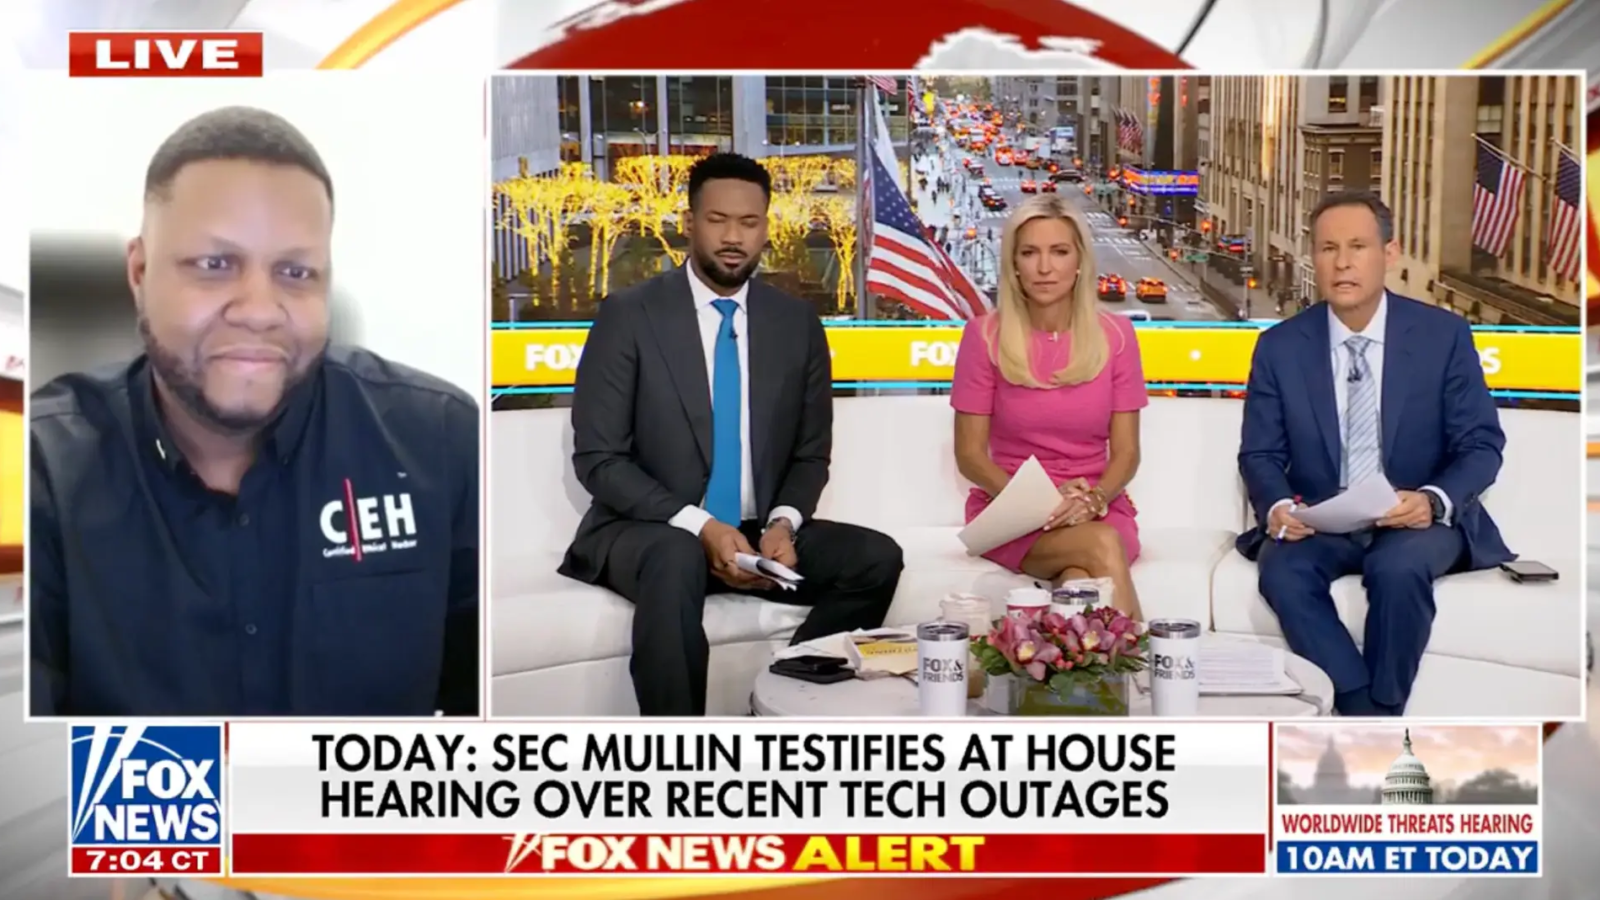
Thank you to Fox News and Fox & Friends for having me on to talk about the cyber incidents and technology disruptions that have been making headlines. I understand why people are concerned. I track cyber threats and have traveled across the United States and internationally to help companies respond after they have been hacked. My message to business owners is simple: take that concern and turn it into action.
Watch my Fox & Friends interview on cyber incidents and business security.
What’s behind the disruptions?
When several major systems have problems close together, it is reasonable to ask whether a cyberattack is involved. In my professional opinion, that possibility deserves serious investigation. But we should not declare every outage an attack without evidence. Software defects, configuration mistakes, aging systems and malicious activity can all cause disruption.
The 2024 CrowdStrike outage is an important example. It affected organizations around the world, but CrowdStrike identified a defective software update as the cause and stated that it was not a cyberattack. The event still showed how much can go wrong when businesses depend on interconnected systems. A failure at one provider can reach airlines, hospitals, banks and smaller companies that have no control over the original problem. CrowdStrike’s incident review.
We cannot personally fix every system behind a national outage. We can make our own businesses harder to compromise and better prepared to keep operating when a provider goes down.
AI has raised the stakes
Cyberattacks are not new. What has changed is how quickly and convincingly attackers can operate. AI can help criminals produce persuasive phishing messages, impersonate trusted people and search for weaknesses at scale. That does not mean every suspicious event is AI driven. It means familiar gaps, including reused passwords and unpatched software, may be found and exploited faster. Australian Cyber Security Centre guidance for small businesses.
Attackers also look for systems that connect to many others. A compromised administrator account, shared network or widely used cloud service can give them access far beyond one computer. Business owners should ask a practical question: If this account or service failed tomorrow, what else would it affect?
Start with the basics you control
Use a unique password for every account. Stop using the same password for email, banking, payroll and business software. A password such as “Foxandfriends2026” may look memorable, but names and predictable patterns make poor choices. Use a password manager to create and store long, unique passwords. NIST recommends passwords of at least 15 characters when you must create one yourself. NIST password guidance.
Turn on multifactor authentication. Where available, use a passkey or security key. If those are not options, an authenticator app is generally a better choice than a text message. Authenticator codes can still be stolen through phishing, so pay attention to unexpected login prompts and review your account recovery settings. CISA mobile security guidance.
Update your devices. This includes computers, iPhones, Android phones, routers and the software your company relies on. Apple has warned that malicious web content has targeted outdated versions of iOS and has urged users to install available updates. Set a routine for checking devices that do not update automatically. Apple’s iPhone security guidance.
Look closely at your network
Some of the risks I see in the field are surprisingly ordinary. A business may rent office space with internet service included and assume its network is private. Another may offer guest Wi-Fi without properly separating visitors from company devices. A new router may be connected before anyone checks its settings, changes its default administrator password or installs current firmware.
Those details matter. Before bringing a router online, confirm who manages it and whether it still receives security updates. Identify which devices and accounts can reach your business systems. Keep guest access separate from sensitive work, and review who can administer the network. If your internet is supplied by a landlord or shared building, ask exactly where your business network begins and what protects it.
IT support is essential. So is testing.
Good IT support keeps systems running, manages updates and helps people when something breaks. Business owners should invest in it. They should also ask whether anyone has tested their defenses from an attacker’s point of view.
That is where penetration testing comes in. With the company’s permission and an agreed scope, an ethical hacker safely tests whether security weaknesses could be used to gain access. The result should be a clear list of findings, prioritized fixes and a plan to check that the fixes worked. Testing can reveal gaps that routine maintenance or automated scans may miss. CISA’s description of penetration testing.
Testing is one part of a larger plan. Businesses also need reliable backups, a way to restore critical work and clear responsibilities when an incident occurs. Ask your team what happens if email, payroll, customer records or internet access becomes unavailable. Then practice the answer before a crisis forces you to improvise.
You do not have to solve every national technology problem to protect the company you have worked hard to build. Start with one account, one device or one network question today. Keep improving from there.
At Firma I.T. Solutions, we help businesses across the country find and address security weaknesses through penetration testing. If you are ready to take a closer look at your defenses, we are ready to help.

