Binance Cyberattack

The $6.34 Billion Binance Hack: How a Fake Job Interview and Internal AI Tool Enabled a Historic Cyberattack

The $6.34 Billion Binance Hack: How a Fake Job Interview and Internal AI Tool Enabled a Historic Cyberattack

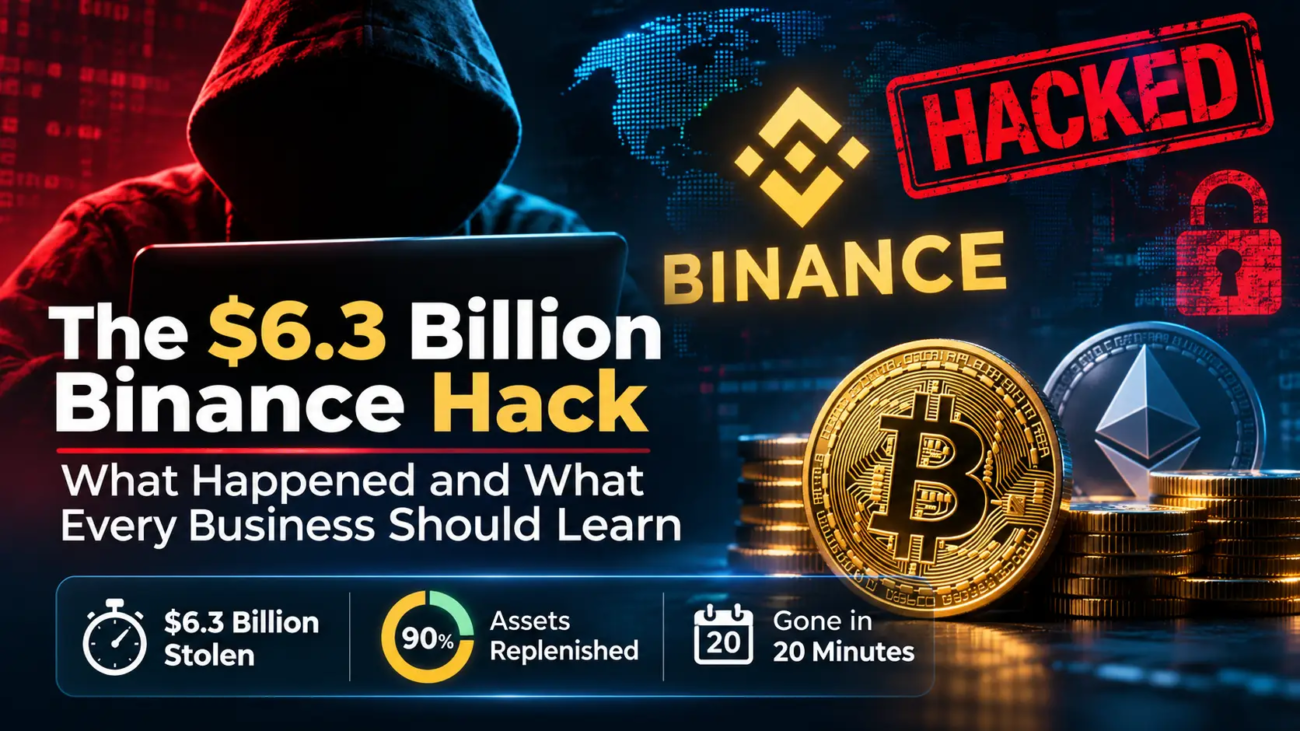
On October 29, 2026, hackers stole approximately $6.34 billion in digital assets from Binance, the world’s largest cryptocurrency exchange. The $6.34 Billion Binance Hack shocked the cryptocurrency industry and raised serious concerns about modern cybersecurity. Investigators soon discovered that the attack involved much more than a weakness in cryptocurrency systems. Cybercriminals had spent months preparing their operation, using malicious software, a fake job interview, stolen credentials, and an internal artificial intelligence (AI) tool.

New findings released by Binance on November 3 revealed how the attackers combined social engineering with weaknesses in the company’s internal systems. The $6.34 Billion Binance Hack demonstrates how several security gaps can create a path to critical business infrastructure. Even organizations with substantial cybersecurity resources can suffer major losses when attackers exploit these weaknesses.

How a Fake Job Interview Enabled the $6.34 Billion Binance Hack

According to Binance’s initial investigation, the attackers began preparing months before the October breach. In June 2026, an engineer responsible for cryptocurrency wallets attempted to install a popular AI coding application. However, the employee unknowingly downloaded a malicious version found through an online search. Binance detected suspicious activity, replaced the computer, and reset the affected credentials. Unfortunately, the attackers had already gathered valuable information about the engineer’s responsibilities and professional relationships.

The attackers used that information to launch a more targeted campaign in September. Someone posing as a recruiter contacted another Binance engineer through a legitimate employment platform. The recruiter arranged what appeared to be a normal hiring process, including interviews with a human resources representative and the company’s supposed CEO. The interviewers used live video, convincing professional profiles, and personal photographs to establish trust. Their approach made the opportunity appear legitimate and reduced the employee’s suspicion.

Near the end of the second interview, the engineer received instructions to download a programming assignment from an online code repository. Software developers often complete similar assignments during job interviews, so the request appeared reasonable. However, the project contained malicious software designed to compromise the employee’s computer. When the engineer opened and initialized the project, the malware connected to a server controlled by the attackers. It also modified a legitimate development component to hide its activity. Binance’s endpoint protection tools initially failed to detect the unfamiliar malware, allowing the attackers to maintain access.

How Internal AI Infrastructure Contributed to the Binance Cyberattack

One of the most concerning findings from The $6.34 Billion Binance Hack involved the company’s internal artificial intelligence infrastructure. On October 20, attackers reportedly used the compromised workstation and an internal AI tool to reach two additional engineers. Both employees worked with Binance’s cryptocurrency wallet systems. During this activity, the attackers obtained a container deployment permission token, giving them another way to access sensitive infrastructure.

This discovery raises concerns for businesses that increasingly rely on AI-powered applications. Many organizations now use artificial intelligence to improve productivity, develop software, analyze information, and automate daily tasks. These tools often connect to internal databases, cloud services, and sensitive business systems. While these connections offer significant benefits, they can also create new security risks when organizations fail to control access.

The Binance incident does not suggest that an AI model independently carried out the attack. Instead, it shows how hackers can exploit access to AI tools during a larger breach. Organizations must carefully manage the permissions they grant these applications. They should also monitor AI activity and limit connections to sensitive systems. Businesses adopting artificial intelligence need to apply the same security standards they use for other critical technology.

How the Attackers Stole $6.34 Billion in Cryptocurrency

After gaining access to several engineering systems, the attackers obtained additional credentials and moved closer to Binance’s cryptocurrency wallets. On October 29, they used stolen credentials and a compromised workstation to deploy a malicious container. This allowed them to gain unauthorized access to an internal service responsible for approving cryptocurrency transfers.

Once the attackers controlled this service, they began transferring digital assets outside Binance’s normal withdrawal process. Within approximately four minutes, five Binance wallets transferred roughly 233 million XRP tokens to an attacker-controlled address. Additional transfers involved Bitcoin, Ethereum, Solana, and other cryptocurrencies. Investigators also found that the attackers abused Ethereum’s EIP-7702 authorization feature. This complicated Binance’s response because suspending customer withdrawals did not automatically cancel the malicious permissions.

Although the largest transfers occurred within minutes, the unauthorized activity continued for several hours. By the time Binance contained the breach, the attackers had stolen approximately $6.34 billion in cryptocurrency. The FBI attributed the attack to North Korean cybercriminals associated with TraderTraitor. Investigators have linked this group to other major cryptocurrency thefts.

Who Was Affected by the Binance Hack, and Will the Money Be Recovered?

The attack caused immediate financial and operational problems for Binance. The company temporarily suspended customer withdrawals while its security teams investigated the breach and secured affected systems. Customers faced uncertainty about accessing their digital assets, while the broader cryptocurrency industry confronted renewed concerns about exchange security.

Binance announced that it would cover the losses rather than pass them to customers. According to its November 3 update, industry partners and investigators had frozen or intercepted approximately $2.85 billion in stolen cryptocurrency. Binance also reported that it had replenished 98% of affected token assets as of October 31.

These figures represent significant progress, but an important distinction remains. Replacing stolen assets with company funds does not mean investigators have recovered that money from the attackers. Binance continues working with law enforcement and industry partners to recover additional funds and strengthen its security.

Cybersecurity Lessons From the $6.34 Billion Binance Hack

The $6.34 Billion Binance Hack demonstrates how cybercriminals have moved beyond traditional phishing emails. Attackers now use legitimate employment platforms, convincing video interviews, and realistic professional identities to gain employees’ trust. Once they establish that trust, they may convince employees to download harmful software or share sensitive information. Businesses must educate their teams about these tactics and establish clear rules for installing software on company devices.

The attack also highlights the growing importance of AI security. As organizations introduce artificial intelligence into daily operations, they must understand how these applications connect to sensitive systems. AI tools should have limited permissions, strong access controls, and continuous monitoring. Business leaders should also consider what an attacker could accomplish after compromising an AI application or its credentials.

Strong internal security controls provide another important layer of protection. Network segmentation, privileged access management, and continuous monitoring help prevent attackers from moving freely through an organization’s systems. A compromised employee computer should not provide unrestricted access to financial records, administrative accounts, or critical infrastructure. Organizations can strengthen these defenses through effective Managed IT Services that support endpoint security, software updates, and ongoing system management.

The incident also reinforces the value of independent security testing. Organizations often invest heavily in firewalls, antivirus software, and other cybersecurity products without confirming whether those defenses work as intended. Comprehensive penetration testing helps identify weaknesses in authentication, network settings, applications, and administrative access. These assessments can also reveal how attackers might combine several vulnerabilities to reach sensitive systems.

The risks extend beyond cryptocurrency companies. As our analysis of the Ernst & Young cyberattack explains, weaknesses involving trusted technology and third-party relationships can expose organizations to serious security threats. Businesses must evaluate the security of both their internal systems and the outside services they depend on.

Why the Binance Hack Should Concern Business Leaders

The $6.34 Billion Binance Hack shows why cybersecurity cannot remain solely an IT department responsibility. The attackers combined human deception, malicious software, compromised AI infrastructure, and stolen credentials to reach critical financial systems. Each weakness helped create the conditions for a devastating breach.

Binance has the financial resources to absorb billions of dollars in losses, but most businesses do not. Even a much smaller attack could disrupt operations, damage customer relationships, and threaten a company’s future. Business owners, executives, and boards of directors must therefore treat cybersecurity as a core business risk.

Protecting an organization requires more than purchasing security software or maintaining cybersecurity insurance. Leaders need to understand where weaknesses exist and whether their security controls can withstand realistic attacks. Regular assessments, employee education, and strong internal safeguards all play important roles in reducing risk.

At Firma IT Solutions & Services, Inc., we help organizations identify cybersecurity weaknesses through comprehensive internal and external penetration testing. Our assessments give business leaders a clearer understanding of potential attack paths and security risks. We also provide practical recommendations that help organizations prioritize improvements and protect critical systems.

The $6.34 Billion Binance Hack reinforces a principle every business should embrace. Installing cybersecurity tools does not automatically make an organization secure. Businesses must regularly test their defenses, correct weaknesses, and adapt as cyber threats evolve.

Trust but verify.

Calling us costs you nothing. Not calling us could cost you everything.

Contact Firma IT Solutions to learn how penetration testing can help protect your organization.

Firma IT Solutions & Services, Inc. — Connected and Protected.
PHP2SHELL_ Global Cyber Threat Alert

PHP2Shell: Critical Cybersecurity Vulnerabilities Threaten Businesses Worldwide

PHP2Shell: Critical Cybersecurity Vulnerabilities Threaten Businesses Worldwide

A critical cybersecurity threat known as PHP2Shell has prompted an urgent warning from the National Security Agency (NSA), raising concerns about the security of millions of websites and business applications worldwide. Two newly disclosed vulnerabilities in PHP, one of the internet’s most widely used programming languages, could allow cybercriminals to take control of vulnerable web servers without requiring a username, password, or prior access.

On October 21, 2026, PHP developers released emergency security patches to address these vulnerabilities. However, businesses that have not updated their systems may remain exposed to potentially devastating cyberattacks.

The NSA has urged organizations to immediately identify vulnerable systems, apply available patches, and increase security monitoring. For businesses that depend on websites, customer portals, and online applications, PHP2Shell represents a serious and immediate cybersecurity risk.

What Is PHP2Shell, and Why Is It Dangerous?

PHP, short for PHP: Hypertext Preprocessor, is a programming language that powers many websites and web applications, including platforms such as WordPress, Drupal, and numerous custom business systems.

PHP2Shell refers to two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, both assigned a CVSS severity score of 9.2 out of 10.

These vulnerabilities affect PHP itself rather than a particular website plugin or application. Successful exploitation could allow an attacker to execute malicious commands on a vulnerable server without authentication.

This is especially dangerous because attackers may bypass application-level security controls and gain access to the underlying server environment.

Once inside, cybercriminals could steal confidential information, modify website content, install malware, disrupt services, or attempt to access other systems connected to the compromised server.

What Systems and Businesses Are Affected?

PHP is widely used across healthcare, financial services, education, retail, government, and professional services.

Potentially affected systems include:

  • WordPress, Drupal, and other PHP-powered websites.
  • E-commerce platforms and online payment applications.
  • Customer and patient portals.
  • Business management applications and administrative dashboards.
  • Web-based APIs and custom applications.
  • Third-party software and hosting environments that depend on PHP.

Businesses using Apache, PHP-FPM, and other PHP deployment environments should verify whether their installations are vulnerable.

Importantly, updating a website’s plugins does not necessarily resolve PHP2Shell. The vulnerabilities exist within the PHP runtime, meaning the underlying software must be patched.

Organizations relying on outside hosting companies or software vendors should request confirmation that the appropriate security updates have been installed.

How Serious Is the PHP2Shell Threat?

The potential consequences are significant.

A successful attack could expose customer information, financial records, login credentials, and sensitive business data. Attackers could also deploy ransomware, interrupt online services, or use a compromised server to move deeper into an organization’s network.

For healthcare organizations, this could threaten protected patient information. Financial institutions could face exposure of confidential records, while retailers and professional service providers could experience operational disruptions and reputational damage.

The situation is particularly concerning because publicly available exploit techniques could enable attackers to automate attacks against vulnerable internet-facing systems.

Security reporting has also identified exploitation attempts occurring before the public disclosure of the vulnerabilities.

According to Reuters, some government websites were temporarily taken offline as organizations worked to protect vulnerable infrastructure.

Although the total number of compromised systems and financial losses remains uncertain, the combination of widespread PHP adoption, critical vulnerability severity, and reported exploitation attempts makes PHP2Shell an urgent cybersecurity concern.

What Is the Resolution?

The PHP development team released emergency patches on October 21, 2026.

Organizations should update to the appropriate fixed versions:

PHP VersionMinimum Patched Release
PHP 8.58.5.12
PHP 8.48.4.27
PHP 8.38.3.36
PHP 8.28.2.35

Businesses running older, unsupported PHP versions should migrate to supported releases or obtain verified vendor-supported security updates.

The NSA also recommends temporarily disconnecting vulnerable systems from the internet when immediate patching is not possible and adequate mitigation cannot be implemented.

However, patching alone may not be sufficient if attackers have already compromised a system. Organizations should investigate suspicious activity and verify that unauthorized access has not occurred.

Six Steps Businesses Should Take Immediately

1. Identify vulnerable systems. Conduct an inventory of websites, servers, applications, and third-party services that depend on PHP. Determine which versions are running and whether they are exposed to the internet.

2. Apply emergency patches. Install the latest security updates and confirm that the correct patched versions are running. Request written verification from hosting providers and technology vendors.

3. Conduct vulnerability scanning and penetration testing. Identify exposed systems and evaluate whether attackers could exploit remaining weaknesses. Penetration testing can also reveal security gaps that might allow attackers to access sensitive data or move through internal networks.

4. Increase cybersecurity monitoring. Review web server logs, application activity, unusual network connections, and unauthorized file changes. Enable enhanced logging and security alerts to detect potential exploitation attempts.

5. Isolate systems that cannot be patched. Temporarily remove vulnerable services from internet access when adequate protection cannot be established. Replace unsupported systems that cannot receive security updates.

6. Investigate potential compromises. If suspicious activity is identified, initiate an incident response investigation. Review affected systems, preserve evidence, rotate compromised credentials, and determine whether sensitive information was accessed.

Why Small Businesses Should Pay Attention

Many small and medium-sized businesses depend on third-party web developers, hosting companies, and IT providers to maintain their technology infrastructure.

Unfortunately, business owners may not know which PHP versions their websites use or whether security patches are being applied.

A website can appear to function normally while remaining vulnerable to attack.

PHP2Shell reinforces the importance of proactive cybersecurity practices, including vulnerability management, regular penetration testing, managed IT services, and documented incident response procedures.

Cybersecurity is not simply about keeping technology operational. It is about protecting the information, systems, and customer relationships that businesses depend upon.

How Firma IT Solutions Can Help

At Firma IT Solutions & Services, we help businesses identify cybersecurity vulnerabilities before attackers can exploit them.

Our penetration testing and managed IT services help organizations evaluate internet-facing infrastructure, identify weaknesses, prioritize security improvements, and strengthen their overall cybersecurity posture.

PHP2Shell demonstrates why businesses cannot afford to wait until a breach occurs before addressing cybersecurity risks.

The most important question is not whether your business uses PHP. It is whether someone has verified that your systems are protected.

Protect your business before cybercriminals find an opportunity.

Firma IT Solutions & Services — Keeps You Connected and Protected.
Website: www.firmaitss.com
Phone: 303-209-0386
Email: admin@firmaitss.com

October-2026-Patch-Tuesday-Alert

Microsoft October 2026 Patch Tuesday: Record 1,400+ Vulnerabilities

This article provides important information about Microsoft’s October 2026 Patch Tuesday updates.

Microsoft October 2026 Patch Tuesday: Record 1,400+ Vulnerabilities

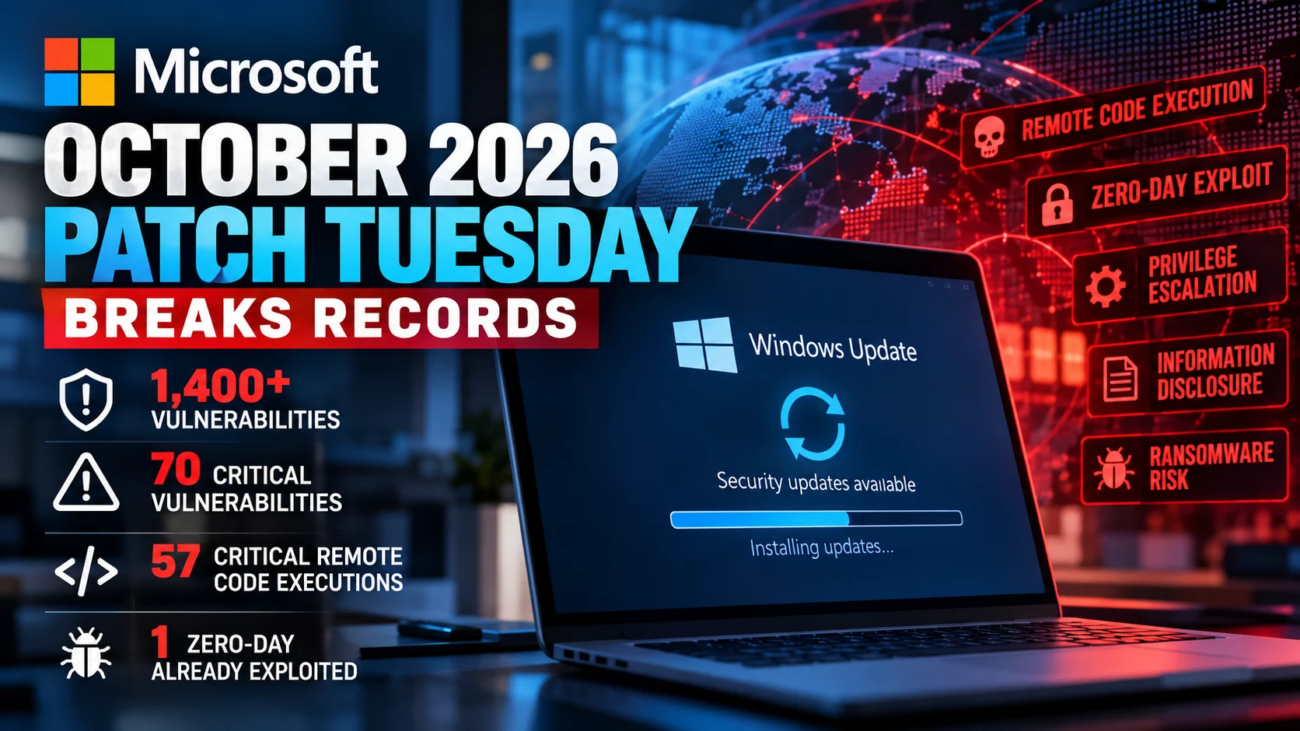
Microsoft October 2026 Patch Tuesday brought a record number of security fixes, giving businesses plenty of reasons to review their defenses. The October 13 release addressed more than 1,400 flaws across Microsoft products. For companies that rely on Windows, Office, SharePoint, and SQL Server, these updates deserve prompt attention.

BleepingComputer counted 1,411 vulnerabilities, including 70 with a Critical rating. Of those Critical flaws, 57 could allow attackers to run harmful code on affected systems. Attackers had already begun exploiting one vulnerability before Microsoft released a fix. Although totals vary by counting method, the scale of this release stands out. BleepingComputer’s report

For business leaders, this release raises a practical question: how quickly can your team identify affected systems and safely update them? Answering that question takes more than turning on automatic updates. It requires a clear device inventory, regular checks, and someone responsible for following up when installations fail.

Understanding the Security Risks

The flaws in October’s release create several paths for attackers. BleepingComputer reported 677 elevation of privilege flaws, 317 remote code execution flaws, and 254 information disclosure flaws. Its count also included 73 denial-of-service flaws, 40 security feature bypass flaws, and 28 spoofing flaws. Each category presents a different risk, from stolen data to lost access to essential services. View the vulnerability breakdown

Remote code execution, often called RCE, can let attackers run harmful instructions on a vulnerable system. Depending on the flaw, an attack might begin with a network request, a harmful document, or another entry point. A successful attack could help criminals install ransomware, steal files, or interrupt daily work.

Consider a medical practice that suddenly loses access to patient records. A similar attack could prevent a law firm from opening case files or meeting a deadline. In either situation, the damage could extend beyond the affected computer. Lost revenue, recovery costs, and damaged client trust can follow.

Elevation of privilege flaws create a different problem. An attacker may gain initial access through an employee’s account and then exploit another flaw to obtain greater control. That access could help the attacker disable security tools, read restricted files, or reach other systems. Limiting account permissions helps reduce this risk, while patching closes known software weaknesses.

Information disclosure flaws can expose private data or reveal details about a system. Even when a flaw does not directly expose client records, it may give attackers useful clues. Those clues can help them plan further attacks against the business. For firms that handle health, legal, or financial records, protecting this information remains a key responsibility.

An Actively Exploited Windows Flaw Adds Urgency

Among October’s fixes, CVE-2026-96951 deserves close attention. The Zero Day Initiative identified this Windows Shell security feature bypass flaw as actively exploited. Its analysis connects the vulnerability to bypassing Mark of the Web protections. Zero Day Initiative’s review

Mark of the Web helps Windows identify files from sources such as internet downloads. Windows uses that information to support security checks and warnings. When attackers bypass those protections, users may face harmful files without the warnings they would normally expect.

This case shows why severity ratings should not be the only factor in patching decisions. A flaw that attackers already use may demand faster action than one with a higher technical score. Businesses should identify affected devices, review Microsoft’s guidance, and test and deploy the relevant updates promptly.

Why Connected Business Networks Face Wider Risk

The Microsoft October 2026 Patch Tuesday release affects products that support everyday business operations. Windows computers, Office applications, SharePoint sites, and SQL Server databases often work together. A weakness in one part of that environment can create risks elsewhere.

The Zero Day Initiative also identified 59 flaws that fit its definition of “wormable.” Such flaws could support attacks that spread without a user signing in or taking action. That finding does not mean worms already exploit these vulnerabilities. However, it highlights why businesses should review exposed services and connected systems carefully. Read the researchers’ analysis

Attackers may combine software flaws with stolen passwords and unsafe settings to expand their reach. As a result, businesses need several layers of protection. Regular updates, limited access, monitoring, and security testing each help address a different part of the risk.

Windows 11 Users Also Face a Support Deadline

October brought another important change for some Windows users. Windows 11 version 24H2 Home and Pro reached the end of updates on October 13, 2026. Businesses still running these editions should move to a supported release. Enterprise and Education editions follow different support schedules, so checking the exact edition matters. Microsoft’s Windows release information

A device inventory provides a useful starting point. Review each computer’s Windows version and edition, then identify which devices need an upgrade. Before making changes, test the software your staff depends on. This helps your team plan the work around business needs and limit downtime.

Turning October’s Updates Into a Practical Action Plan

The first step is to match the October updates to the systems your business uses. Give prompt attention to actively exploited flaws, servers that face the internet, and systems that handle sensitive data. Testing can help catch compatibility problems, but the process also needs clear deadlines and follow-through.

Next, confirm that updates actually installed. Automatic updates can fail, and some devices remain offline for long periods. Others need a restart before a patch takes effect. A central patch management tool can help your team find missed updates and track devices that still need attention.

Account access also deserves review. Employees should have the permissions their jobs require, and administrator rights should have a clear business purpose. Remove unused accounts, review remote access tools, and use multifactor authentication to help protect sign-ins. These steps help limit what an attacker can do after gaining access.

Security testing provides another layer of insight. Updates fix known software flaws, but they do not resolve every weak password, exposed service, or unsafe setting. A vulnerability assessment helps identify known weaknesses. Penetration testing examines how attackers might exploit gaps in your defenses. The findings should lead to clear priorities, assigned owners, and checks that confirm each fix works.

Finally, review your response and recovery plans. Test whether your team can restore key files and systems from backups. Make sure employees know how to report suspicious activity and who will coordinate the response. Clear roles can reduce confusion when an incident disrupts normal work.

What This Means for Small and Medium-Sized Businesses

Small businesses use many of the same Microsoft products as large companies, but they often have fewer IT resources. A law firm with 20 employees still needs secure access to client files. A medical practice with 50 workstations still needs reliable systems to support patient care.

For these businesses, a long outage can place immediate pressure on staff, revenue, and client relationships. Recovery may also require outside help and time away from daily work. A consistent security routine helps reduce that exposure.

That routine should fit the size and needs of the business. Keep track of devices, review updates, limit access, and test backups. When internal staff lack the time or skills to manage these tasks, outside IT support can help maintain steady oversight.

How Firma IT Solutions Helps Businesses Stay Protected

At Firma IT Solutions & Services, Inc., we help businesses find security weaknesses and take practical steps to address them. Our cybersecurity and managed IT services include penetration testing, vulnerability identification, patch management, endpoint management, and ongoing IT support.

Our internal and external penetration tests examine weaknesses that attackers might exploit. We provide technical findings for IT teams and clear reports for business leaders. These reports help connect security issues to business risks, giving your team a stronger basis for deciding what to fix first.

We also help businesses manage updates and improve their daily IT practices. Keeping systems protected requires regular attention, clear ownership, and checks that confirm the work is complete. Those habits support a more reliable technology environment.

Build Security Into Everyday Business Operations

Microsoft October 2026 Patch Tuesday shows why security needs a place in routine business planning. Installing updates is an essential first step, followed by checks that confirm devices received the fixes. Access reviews, threat monitoring, backup testing, and regular security assessments help address the remaining gaps.

Businesses can make this work more manageable by assigning clear responsibilities and setting a regular schedule. Over time, consistent attention helps teams find problems earlier and respond with greater confidence.

At Firma IT Solutions, we believe: If It’s Untested, It’s Unprotected.

Protect Your Business With Firma IT Solutions

Knowing that updates exist is only part of protecting your business. You also need to know which devices remain exposed and whether your security controls work as expected. Firma IT Solutions & Services helps businesses answer those questions through practical testing and ongoing IT support.

Whether you need penetration testing, help managing updates, or broader managed IT services, our team can help you plan your next steps. Contact Firma IT Solutions today to discuss your business’s security needs.

Firma IT Solutions & Services, Inc.
Phone: 303-209-0386
Email: newbiz@firmaitss.com
Website: www.firmaitss.com

Keeps You Connected and Protected.
If It’s Untested, It’s Unprotected.

computer

Apple Just Released iOS 27 and macOS 27: Why You Should Update Now

Apple released its newest operating systems on September 14, 2026, including iOS 27, iPadOS 27, macOS 27 Golden Gate, watchOS 27, and tvOS 27. While many people will update because of new features, there is another major reason businesses and consumers should pay attention: cybersecurity.

Apple addressed an unusually large number of security vulnerabilities in this release cycle. iOS 27 and iPadOS 27 address approximately 126 unique CVEs, while macOS 27 Golden Gate addresses approximately 210 vulnerabilities. Apple also released iOS 26.7 and macOS Tahoe 26.7 for users who are not immediately moving to the newest major operating system.

From a cybersecurity perspective, this is not an update that should simply be ignored.

Why Upgrade to iOS 27?

iOS 27 is compatible with the iPhone 11 and newer, including the iPhone SE 2nd and 3rd generations. However, not every iOS 27 feature works on every compatible iPhone. The most advanced Apple Intelligence and Siri AI capabilities require newer hardware, including the iPhone 15 Pro and Pro Max and newer supported models.

Beyond security, these are five of the biggest iOS 27 features getting attention:

  1. Siri AI and the new Apple Intelligence experience. Siri has received a major redesign with better conversational abilities, personal-context awareness, onscreen awareness, and the ability to perform actions across applications. Siri can help locate information in messages, email, photos, and other areas of your device. Apple has also introduced Write with Siri and deeper Visual Intelligence capabilities. 
  2. Major improvements to Photos. Apple Intelligence introduces Spatial Reframing, an Extend tool that can intelligently expand images beyond their original borders, and an upgraded Clean Up feature for removing unwanted objects more naturally. 
  3. A smarter Safari browser. Safari can automatically organize tabs by topic, monitor websites for changes such as product availability or price changes, and even create certain customized extensions based on natural-language descriptions. 
  4. Better performance and connectivity. Apple says iOS 27 improves app-launch performance, photo loading, AirDrop transfers, search, and transitions between Wi-Fi and cellular networks. These improvements may be particularly noticeable on older supported devices. 
  5. Improved Screen Time and child-safety controls. New features include Ask to Browse, stronger Communication Safety protections, app Time Allowances, scheduling controls, and redesigned Screen Time settings. 

There are also smaller improvements, including independent alarm and timer volume settings, improved iCloud Shared Albums, new AirPods audio controls, and refinements to Apple’s Liquid Glass interface.

The Cybersecurity Reason to Update

The biggest reason Firma IT Solutions recommends keeping operating systems current is security.

Apple’s iOS 27 security advisory identifies more than 120 vulnerabilities across components including Bluetooth, CoreMedia, the kernel, authentication services, WebKit, Wi-Fi, Siri, Shortcuts, and networking.

Apple does not assign every vulnerability a simple “critical” rating, but several have particularly serious potential impact.

One example is CVE-2026-84607, which affected the AVEVideoEncoder component. Apple says a sandboxed application could potentially execute arbitrary code with kernel privileges. Kernel-level vulnerabilities are particularly serious because the kernel operates at one of the most privileged levels of the operating system.

Another significant issue, CVE-2026-65414, affected Bluetooth. Apple says a remote attacker could potentially cause application termination or arbitrary code execution.

A CoreMedia vulnerability, CVE-2026-64752, could allow a maliciously crafted image to result in arbitrary code execution. The issue was significant enough that Apple addressed it by removing the vulnerable code. 

Apple also corrected CVE-2026-65329, a networking vulnerability that could allow an attacker in a privileged network position to bypass IPsec authentication and potentially intercept network traffic.

Finally, CVE-2026-84523 affected Apple’s APFS file system. Apple says an application could potentially cause system termination or write to kernel memory.

Apple has not indicated that these particular iOS 27 vulnerabilities were being actively exploited when the update was released. Nevertheless, once vulnerabilities and patches become public, attackers have additional information they can use to investigate systems that remain unpatched.

What About iOS 26.7?

Apple released iOS 26.7 at the same time as iOS 27. It addresses approximately 82 unique CVEs.

An important clarification: on the iPhone, iOS 26.7 is not simply for devices incapable of running iOS 27. Both releases support the iPhone 11 and newer. Apple is allowing users to remain on iOS 26 temporarily while still receiving an important security update. However, iOS 27 includes additional security fixes that are not included in iOS 26.7. 

For businesses, that means remaining on iOS 26.7 may make sense temporarily while confirming application compatibility, but it should not be interpreted as identical security coverage.

Which Devices Cannot Upgrade?

For iPhones, iPhone XS, iPhone XS Max, iPhone XR, iPhone X, iPhone 8, and earlier generations cannot install iOS 27. The supported lineup begins with the iPhone 11 and iPhone SE 2nd generation.

Some older iPads can install iPadOS 26.7 but cannot install iPadOS 27. The cutoff for iPadOS 27 is iPad Pro 12.9-inch 4th generation, iPad Pro 11-inch 2nd generation, iPad Air 4th generation, standard iPad 9th generation, and iPad mini 6th generation or newer.

The situation is even more significant for Mac users.

macOS 27 Golden Gate supports Apple-silicon Macs only. Intel-based Macs cannot install macOS 27. Apple states that any Mac using an M-series or supported A-series Apple chip can upgrade.

Several of the final Intel Macs can still run macOS Tahoe 26.7, including the 2019 16-inch MacBook Pro, certain 2020 Intel MacBook Pros, the 2020 27-inch iMac, and the 2019 Mac Pro.

Apple is continuing to release security updates for older macOS versions, but organizations should not assume that means exactly three additional years of complete security coverage. Apple specifically warns that not all known security issues are necessarily addressed in previous versions of its operating systems.

What Businesses Should Do Now

Whether your organization uses Macs, iPhones, or iPads, operating-system updates should be part of your cybersecurity program—not something left entirely to individual employees.

Organizations should inventory their Apple devices, identify which systems can upgrade to the newest operating systems, install available security updates, and develop replacement plans for hardware approaching the end of operating-system support.

Software updates close vulnerabilities that Apple already knows about. Penetration Testing answers a different question: What vulnerabilities still exist in your environment that attackers could actually exploit?

Firma IT Solutions provides professional Penetration Testing and Managed IT Services to help organizations identify weaknesses, reduce cybersecurity risk, and keep systems secure.

If it’s untested, it’s unprotected.

For information about Penetration Testing or Managed IT Services, contact Firma IT Solutions at 303-209-0386 or visit firmaitss.com.

Firma IT Solutions — Keeps You Connected and Protected.
Designer (6)

CMMC Phase II Requirements Suspended

CMMC Isn’t Dead. But the Rules Just Changed.

For years, I’ve been telling business leaders that cybersecurity isn’t optional if you’re doing business with the federal government. In light of the recent CMMC Phase II Requirement Suspended announcement, it’s more important than ever to stay informed. Whether you’re a prime contractor or a subcontractor, protecting sensitive government information isn’t just a best practice—it’s a requirement.

That’s why the Department of War’s announcement on July 13, 2026, caught the attention of the entire Defense Industrial Base. The department suspended the implementation of CMMC Phase II requirements and launched a comprehensive review of the Cybersecurity Maturity Model Certification (CMMC) program. Before anyone starts celebrating or assumes cybersecurity requirements have disappeared, let’s talk about what actually happened and what it means for organizations that want to continue doing business with the federal government.

What Happened?

The Department of War announced the immediate suspension of CMMC Phase II requirements, which were scheduled to become effective on November 10, 2026. At the same time, it created a CMMC Review and Reform Task Force to examine the program and recommend changes. The stated goal is to reduce barriers to entry for small, medium-sized, and non-traditional defense contractors while maintaining an acceptable cybersecurity baseline.

This decision does not eliminate CMMC altogether. It pauses the next phase of implementation while leadership reevaluates how cybersecurity compliance is validated throughout the defense supply chain.

What Changed?

The biggest change is that organizations that were preparing for mandatory Phase II certification requirements now find themselves in a holding pattern.

Under the original roadmap, many contractors handling Controlled Unclassified Information (CUI) would eventually need third-party assessments and certifications to demonstrate compliance. That implementation has now been suspended pending review. The department has indicated it wants to identify ways to reduce compliance complexity and lower the cost of participation for defense contractors.

In simple terms, the government hit the pause button on additional certification requirements—not on cybersecurity itself.

What Remains in Effect?

This is the part many businesses are overlooking.

The cybersecurity requirements have not gone away.

Phase I self-assessment requirements remain in force. Contractors are still expected to safeguard Federal Contract Information (FCI) and Controlled Unclassified Information (CUI). Organizations handling CUI are still expected to comply with NIST SP 800-171 requirements, and the government can still validate cybersecurity compliance through self-assessments and selected government-led reviews. Existing DFARS cybersecurity obligations also remain unchanged.

If your organization stopped investing in cybersecurity because you heard “CMMC was suspended,” you’re misunderstanding the announcement.

Compliance verification may be changing. Cybersecurity expectations are not.

Why Did They Do It?

According to department leadership, the review is intended to reduce bureaucracy, accelerate acquisition timelines, and make it easier for smaller businesses to compete for federal contracts. Officials expressed concern that the cost and complexity of compliance could discourage innovative companies from participating in the defense supply chain.

I understand that concern.

Many small businesses struggle with the expense of assessments, policy development, security tools, documentation, and ongoing compliance management. For some organizations, the cost of certification has felt like a barrier to entry rather than a security improvement.

The challenge for the government is finding the right balance between accessibility and security.

What Does This Mean for Contractors?

My advice to contractors is simple: stay the course.

If you’ve been working toward NIST 800-171 compliance, continue. If you’ve invested in security controls, employee awareness training, vulnerability management, multi-factor authentication, endpoint security, and incident response capabilities, don’t stop now.

Organizations that pause their cybersecurity initiatives because certification requirements are under review may create significant risk for themselves. The government has made it clear that protecting federal information remains a non-negotiable requirement.

Contractors should continue:

  • Maintaining NIST 800-171 compliance efforts.
  • Performing required self-assessments.
  • Maintaining accurate SPRS reporting where applicable.
  • Improving documentation and security processes.
  • Preparing for future certification requirements that may emerge from the review.

The organizations that remain proactive will be in the best position regardless of what the final version of CMMC looks like.

What Does This Mean for Cybersecurity?

This is where things get interesting.

For years, one of the biggest criticisms of the defense supply chain has been that cybersecurity often relied on self-attestation rather than independent validation. CMMC was designed to address that concern by introducing varying levels of assessment and verification.

By suspending Phase II requirements, the government is signaling that it wants to rethink how cybersecurity assurance is measured while reducing unnecessary burden on contractors. Whether this ultimately strengthens or weakens cybersecurity will depend on what replaces the current approach.

What should not be lost in this discussion is the reality that nation-state adversaries, ransomware groups, and cybercriminals are not pausing their attacks while the government reviews CMMC. Sensitive data remains valuable. Supply chain attacks remain common. The threat landscape remains aggressive.

The organizations that view cybersecurity only as a compliance exercise will always struggle. The companies that view cybersecurity as a business imperative will continue protecting their customers, their reputation, and their federal contracts regardless of what acronym appears in the regulations.

Final Thoughts

CMMC is not dead. It’s being reexamined.

The Department of War has paused Phase II certification requirements, but the obligation to protect federal information remains fully intact. Contractors should not interpret this announcement as permission to slow down cybersecurity investments. In my opinion, the smartest organizations will continue building mature security programs, maintaining NIST 800-171 compliance, and preparing for whatever version of CMMC emerges from this review process.

Because at the end of the day, compliance may change. Threat actors won’t.

ChatGPT Image Jun 25, 2026, 02_04_42 PM

HOW CRUCIAL IS CONTINUOUS MONITORING IN MAINTAINING NETWORK SECURITY IN DENVER?

In Denver’s evolving cyber landscape, you can’t afford to let your guard down for a second. Continuous network monitoring has become absolutely essential, with real-time analysis catching threats before they become disasters. Our city’s businesses and infrastructure rely on 24/7 vigilance, identifying vulnerabilities and stopping breaches in their tracks. Through sophisticated monitoring systems and integrated threat intelligence sharing, Denver’s approach to network security transforms raw data into actionable protection. There’s so much more to discover about safeguarding your digital assets.

Key Takeaways

  • Denver’s real-time network analysis enables immediate threat detection, preventing breaches before they can cause significant damage.
  • Continuous monitoring provides 360-degree visibility across network infrastructure, ensuring comprehensive protection of Denver’s digital assets.
  • The city’s threat intelligence sharing system strengthens collective defense through real-time collaboration with neighboring businesses.
  • Proactive monitoring helps identify and respond to APT attacks targeting Denver’s technology and financial sectors.
  • Denver’s Network Operations Center demonstrates how continuous assessment effectively streamlines security protocols and compliance management.

The Critical Role of Real-Time Network Analysis in Denver

real time network security vigilance

While many cities struggle with cybersecurity, I’ve seen firsthand how Denver’s commitment to real-time network analysis has transformed our approach to digital safety. You’ll appreciate how we’ve augmented monitoring effectiveness through continuous threat detection, catching potential breaches before they happen. Our approach leverages 360-degree visibility across the entire network infrastructure to ensure no vulnerabilities go unnoticed.

Trust me, I’ve watched our team optimize resource utilization by strategically deploying security measures where they’re needed most. Understanding network representations and implications helps us better analyze and secure our city’s digital infrastructure. We’ve integrated threat intelligence sharing with neighboring businesses to strengthen our collective defense capabilities. The implementation of behavioral analysis enables us to quickly identify and respond to suspicious network activities.

When you’re protecting a city’s digital infrastructure, every second counts. That’s why I’m proud of how we’ve integrated AI-driven analytics with our GIS systems. It’s like having a guardian that never sleeps, always watching over Denver’s digital landscape.

Strengthening Cybersecurity Through Continuous Assessment

Nearly every security expert I’ve met agrees that continuous assessment is the bedrock of modern cybersecurity. I’ve seen firsthand how Denver businesses thrive when they adopt ongoing security risk analysis. You’ll want to implement continuous monitoring because it lets you spot threats before they become disasters. Real-time threat detection enables organizations to respond swiftly and contain potential breaches before they escalate. Intrusion detection systems have become essential tools for maintaining strong network security.

Through my work with local companies, I’ve learned that proper asset prioritization makes all the difference. You can’t protect everything equally, and that’s okay. Instead, focus your resources where they matter most. Regular tabletop exercises are essential for validating your security monitoring effectiveness. Trust me, when you’re constantly evaluating your security posture, you’ll sleep better knowing your network is protected around the clock. Web application testing has become crucial for businesses seeking to maintain comprehensive security coverage in Denver and Colorado Springs.

Building Effective Response Strategies for Network Threats

continuous proactive network monitoring

Since I started consulting for Denver tech companies, I’ve learned that having a solid response strategy isn’t just nice to have – it’s essential for survival. You’ve got to adopt proactive risk mitigation before threats hit your doorstep. I’ve seen too many companies scramble when they should’ve had thorough incident planning in place. Today’s sophisticated APT attackers are increasingly targeting Denver’s thriving tech and finance sectors. Critical infrastructure protection becomes paramount as municipalities manage essential utilities and public safety systems. Regular assessments reveal that human elements account for over 82% of security breaches in organizations.

Trust me, you’ll want to build your response strategy around clear protocols and regular team training. I recommend starting with threat identification, then developing specific response procedures. Don’t forget to collaborate with local cybersecurity experts – they’re an indispensable resource for strengthening your defense posture. Organizations should conduct regular security audits to identify and fix potential network vulnerabilities before they can be exploited.

Denver’s Approach to Security Documentation and Policy Management

Denver’s approach to security documentation and policy management has transformed dramatically in my 15 years consulting here. I’ve watched companies evolve from basic security checklists to sophisticated frameworks that blend SOC2, ISO 27001, and other standards. You’ll find that policy implementation isn’t just about ticking boxes anymore – it’s about creating a living security ecosystem. The airport’s Network Operations Center serves as a crucial model for implementing comprehensive security documentation across the city. Local manufacturers are increasingly implementing compliance management software to streamline their security protocols and reporting requirements. Construction firms now prioritize data breach prevention through robust documentation systems to protect valuable project intellectual property. Our team conducts thorough Pen Testing to identify vulnerabilities in organizations’ security documentation frameworks.

What excites me most is how local businesses have adopted security awareness training. I remember struggling to convince executives about its importance back in 2008. Now, they’re leading the charge, collaborating with their boards to establish robust risk management strategies that actually work.

Advancing Network Protection Through Education and Innovation

educating tomorrow's cybersecurity defenders

While technology evolves at breakneck speed, I’ve noticed a remarkable shift in how we approach network protection through education here in Colorado. Our emerging cybersecurity curriculum has transformed how we defend against threats, and I’m thrilled to see students diving into hands-on learning. Educational institutions have become increasingly vulnerable as they face ransomware threats at an alarming rate. Student data protection has become paramount as institutions work to maintain operational continuity and academic integrity.

You’ll find our local student cybersecurity competitions drawing bigger crowds each year. Just last month, I watched teams from Denver tackle real-world scenarios with impressive skill. It’s not just about learning – it’s about building a community of defenders. Through partnerships with tech firms and practical workshops, we’re equipping the next generation with tools they’ll need to protect our digital future. The implementation of zero trust architecture has become a cornerstone of our educational approach to network security. Regular penetration testing helps identify vulnerabilities before malicious actors can exploit them.

Frequently Asked Questions

How Much Does Implementing Continuous Monitoring Typically Cost for Small Denver Businesses?

You’ll typically invest $100-150 per seat monthly for basic monitoring, but your total costs depend on your budget considerations and resource allocation. Additional services or specialized support can raise costs to $200+ per seat.

Which Certifications Are Required for Continuous Monitoring Specialists in Denver?

Imagine mastering your cybersecurity destiny! You’ll need GIAC GMON or CompTIA CySA+ certifications, plus ongoing training requirements in risk assessment strategies. Denver doesn’t mandate specific certs, but these credentials boost your professional value.

Can Continuous Monitoring Systems Be Effectively Managed Through Remote Work Arrangements?

Yes, you’ll find remote workflow optimization highly effective for managing continuous monitoring systems. With proper employee engagement considerations and digital tools, you can successfully oversee security operations from anywhere while maintaining operational excellence.

What Percentage of Denver Organizations Currently Utilize Continuous Monitoring Technologies?

While exact Denver stats aren’t available, you’ll find most organizations adopt continuous monitoring for network security compliance. Denver cybersecurity trends suggest widespread implementation, especially among businesses prioritizing robust security measures and regulatory requirements.

How Long Does It Take to Fully Implement a Continuous Monitoring System?

Like nurturing a garden, you’ll find your continuous monitoring system takes 6-12 months to fully bloom. Your implementation timeline depends on system complexity and personnel training requirements, but you’ll gain security independence.

Conclusion

Just like a vigilant night watchman can’t protect a building by doing occasional walk-throughs, you can’t secure Denver’s networks through sporadic monitoring. You’ll need 24/7 surveillance to catch threats in real-time. With cyber attacks in Denver increasing by 47% last year, your continuous monitoring system acts as your digital security camera – always watching, always protecting. It’s no longer optional – it’s your front line of defense in today’s cyber battlefield.

Designer (2)

The Breach Era We’re Living in

The Breach Era We’re Living In

We no longer live in a time when breaches show up as isolated incidents every few months. Today, organizations face a constant stream of attacks that move faster and reach deeper than most leaders expect. What we are seeing now is systemic, continuous, and scaling at a pace that forces a very different conversation. This reflects The Breach Era We’re Living In, where these threats have become the new normal.

Over the past few weeks alone, breaches have hit infrastructure, identity systems, SaaS platforms, biometrics, and even government environments. On the surface, each incident looks unique. However, when you step back and evaluate them through a practitioner’s lens, the pattern becomes clear. The issue is not that attackers have become unstoppable. The issue is that they are testing at a level most organizations never match.

In simple terms, organizations are not being outmatched. They are being out-tested.


Five Breaches, One Clear Pattern

Start with the Fortinet breach. Attackers compromised thousands of firewall devices and used valid credentials to gain entry into enterprise environments. Instead of causing immediate disruption, they moved quietly, working their way into authentication systems and building long-term access. This was not noise. It was control.

Now look at the massive credential dataset discovered shortly after. Attackers collected billions of usernames and passwords and tied them to live systems. Instead of storing that data for later use, they aligned it with active vulnerabilities and launched attacks in real time. That shift should get every leader’s attention, because it turns stolen data into immediate weaponization.

Then there is the Madison Square Garden breach, which exposed biometric data tied to millions of individuals. This changes the stakes entirely. When passwords are compromised, you reset them. When biometric data is exposed, that risk does not go away. It follows the individual indefinitely, and it introduces long-term legal and privacy implications.

The Klue breach tells another important story. By compromising a single SaaS platform, attackers gained access to multiple organizations. This is how modern attacks scale. Instead of targeting one company at a time, attackers target shared systems and trust relationships that connect entire ecosystems.

Finally, the Texas government breach reinforces something we have known for years but have not fully addressed. Third-party vendors remain one of the most reliable entry points. Attackers used a connected system to expose millions of sensitive records. That is not just a perimeter failure. That is a visibility problem across the extended environment.

Individually, each of these breaches is significant. Together, they tell us exactly where we are.


The Illusion of Security

Many organizations believe they are secure because they have invested in the right tools. Firewalls are configured. Endpoint protection is deployed. Multi-factor authentication is enabled. On paper, everything looks solid.

However, the breaches we are seeing today are not bypassing those controls. They are operating within them.

Attackers are logging in with valid credentials. They are leveraging trusted integrations. They are navigating systems that behave exactly as designed. From the system’s perspective, nothing looks wrong. That is exactly why these attacks succeed.

The real problem is not a lack of technology. The real problem is a lack of validation. Too many organizations assume their controls work, but they have never tested them under real-world conditions.


Where Organizations Fall Short

Most security programs focus on prevention and compliance. They check for proper configurations, confirm that controls exist, and ensure that systems meet requirements.

Attackers take a completely different approach.

They test whether stolen credentials give them access. They explore how far they can move once inside. They identify which systems hold valuable data and whether anyone will stop them.

If organizations are not asking those same questions, then they are leaving critical gaps behind. Those gaps do not stay hidden forever. An attacker will find them eventually.


Why Penetration Testing Changes the Equation

Penetration testing forces organizations to move from assumption to proof. It shows how systems behave under pressure and how an attack actually unfolds.

More importantly, it answers the question that matters most. If an attacker gets in today, what happens next?

In a scenario like the Fortinet breach, penetration testing simulates the use of valid credentials. It shows how easily an attacker can gain access and what systems become reachable once they do. It also reveals how far that access extends, whether into identity systems, privileged accounts, or sensitive data stores.

This is where penetration testing creates real value. It does not just identify isolated issues. It connects those issues into complete attack paths. It shows how a small weakness can lead to a major compromise when exploited in sequence.

That level of visibility is what most organizations are missing.


Testing the Modern Attack Surface

Today’s environments are highly connected. Organizations rely on SaaS platforms, APIs, and vendor integrations to operate at scale. These connections create efficiency, but they also create opportunity for attackers.

Penetration testing brings those connections into focus. It evaluates how systems interact, how data flows, and where trust exists between platforms. It tests whether those trust relationships can be abused in the same way attackers would attempt.

At the same time, penetration testing helps organizations understand what data truly matters. Not all data carries the same level of risk. Sensitive data such as healthcare records, financial information, or biometric identifiers requires stronger protection.

Understanding where that data lives and how it can be accessed is critical. Without that visibility, organizations cannot prioritize what they need to defend.


A Shift in Leadership Thinking

Leaders need to rethink how they define security readiness. The question is no longer whether controls are in place. The real question is whether those controls have been proven under pressure.

Security is not static. It requires continuous validation.

Attackers already operate this way. They test environments every day. They automate credential attacks, scan for weak configurations, and probe for trust relationships they can exploit.

If organizations are not testing at the same level, they will always be one step behind.

Penetration testing helps close that gap. It allows organizations to see their environment through an attacker’s lens and take action before a breach occurs.


Final Thought

Every breach we discussed points to the same underlying issue. Attackers succeed because organizations have not tested their environments in a way that reflects how real attacks happen.

That is the gap.

Penetration testing closes that gap by exposing weaknesses early and showing how attackers can move through an environment. It provides clarity, not guesswork.

At the end of the day, organizations do not rise to the occasion during a breach. They fall back on the level of testing they have done beforehand.

Right now, the organizations that are winning are the ones willing to test themselves before someone else does.

Designer (3)

The Fortinet Breach: A Wake-Up Call for How Modern Attacks Really Work

The Fortinet Breach: A Wake-Up Call for How Modern Attacks Really Work

By Rodney Gullatte Jr.

In this article, we take a closer look at the recent Fortinet Breach and its implications.

The recent Fortinet breach is more than another cybersecurity headline. It clearly shows that attacker behavior has changed, and many organizations still have not adjusted. At its core, this breach reveals a gap that leaders continue to overlook.

This situation is not about perimeter failure. Instead, it highlights validated access at global scale.


What Actually Happened

In June 2026, researchers uncovered a large-scale compromise involving Fortinet firewall devices. Attackers breached nearly 74,000 internet-facing systems across more than 21,000 organizations in 194 countries.

More importantly, the attackers did not just gain access. They captured plaintext credentials, which gave them immediate, usable entry into these environments.

From there, the attackers moved deeper into networks. They accessed centralized authentication systems like RADIUS servers and Microsoft Active Directory. As a result, they positioned themselves inside the identity layer of enterprise environments.

This was not a quick grab for data. Instead, attackers took a controlled and deliberate approach to gain long-term access.


Why This Breach Matters

This breach stands out because it changes how we think about risk.

First, the scale matters. The number of affected devices shows that this issue spans industries and borders. Healthcare, finance, government, and enterprise organizations all face the same exposure.

Second, this attack reinforces a shift that security leaders have warned about for years. Attackers no longer focus on breaking through defenses. Instead, they focus on logging in with legitimate credentials.

When attackers use valid credentials, systems treat them as trusted users. As a result, traditional defenses often fail to detect them.

Finally, the breach shows how attackers maintain persistence. Once inside authentication systems, they no longer operate at the edge. Instead, they become part of the environment itself, which makes detection much harder.


The Real Problem: Assumed Security

Many organizations believe they are secure because they have deployed the right tools. Firewalls are configured. Endpoint protection is active. Multi-factor authentication is enabled.

However, those controls create a false sense of confidence when organizations do not test them properly.

The Fortinet breach proves this point. The attackers used real credentials. The systems responded exactly as designed. Access worked as expected.

That is exactly why the attack succeeded.

Security teams did not fail to deploy controls. Instead, they failed to validate how those controls behave under real-world attack conditions.


Why Penetration Testing Matters Now

Penetration testing changes the conversation from assumptions to evidence. It forces organizations to see how their environment performs under pressure.

More importantly, it answers a critical question. If an attacker gains access today, what happens next?

In the Fortinet scenario, penetration testing could have exposed several key risks early. For example, it could have shown how easily valid credentials provide access to external systems. It also could have mapped how far an attacker could move once inside the network.

Additionally, penetration testing would show which systems and data become reachable after initial compromise.

These insights matter because they reflect exactly how attackers operate.

Penetration testing does more than identify individual weaknesses. It demonstrates how attackers chain those weaknesses together. It shows the real path from entry to impact.

In cases like this, where attackers moved into authentication systems, a strong penetration test reveals critical gaps. These gaps often include poor segmentation, excessive permissions, limited visibility, and weak detection controls around legitimate access.

As a result, organizations gain clarity into risks that traditional tools often miss.


A Shift in How Leaders Think About Security

The Fortinet breach should push every organization to rethink how it measures security.

Security does not come from the tools you deploy.
Security comes from what you have tested and proven.

At the same time, attackers already test environments every day. They search for weak credentials, misconfigurations, and trust relationships they can exploit. They use automation and scale to their advantage.

If organizations do not match that level of testing, they fall behind.

Penetration testing helps close that gap. It aligns defensive strategies with real attacker behavior. It gives organizations a clear view of how their environment appears to an adversary.


Final Thought

The Fortinet breach is not just a technical issue. It reflects a larger problem across the cybersecurity landscape. Too many organizations rely on assumptions instead of evidence.

Attackers do not assume. They test.

That leaves every organization with one simple question.

Are you doing the same?

Because in today’s environment, the organizations that test themselves thoroughly are the ones that can fix weaknesses before they turn into public incidents.

advanced_network_security_strategies_gl0ia

BEYOND THE FIREWALL: PROTECTING CUSTOMER DATA WITH ADVANCED NETWORK PENETRATION STRATEGIES

You can’t rely on firewalls alone to protect customer data in today’s threat landscape. Modern attacks bypass traditional defenses through AI-powered techniques and social engineering. Firma IT Solutions, with over 20 years of experience and a 4.8 Google rating, specializes in certified network penetration testing and ethical hacking to identify these vulnerabilities. To stay ahead, you’ll need a multi-layered approach: implement continuous monitoring systems, conduct regular penetration testing, and maintain strict access controls. Zero-trust architecture and advanced authentication help prevent lateral movement by attackers. The journey to true data security requires going far beyond basic perimeter defenses. Call now for your initial assessment and protect your customer data with industry-leading expertise.

Key Takeaways

  • Implement continuous AI-powered monitoring systems to detect and respond to suspicious network activity in real-time.
  • Deploy zero-trust architecture requiring authentication for all access attempts, preventing unauthorized lateral movement within networks.
  • Conduct regular penetration testing with clear objectives to identify vulnerabilities before attackers can exploit them.
  • Apply robust encryption protocols for customer data both in transit and at rest across all network segments.
  • Establish automated incident response systems that can instantly detect, isolate, and neutralize potential security threats.

Understanding Modern Network Security Challenges

While I’ve spent years helping organizations protect their networks, I’ve never seen security challenges evolve as rapidly as they’re now in 2025.

You’re facing a perfect storm – over 30,000 vulnerabilities each year, and attackers who can strike within hours of finding a weakness. Trust me, I’ve learned the hard way that traditional defenses just don’t cut it anymore.

Your vulnerability assessment needs to be smarter and faster than ever. Modern security requires AI-powered monitoring systems to detect and respond to threats in real-time. Organizations must embrace zero-trust architecture to ensure continuous verification of all access attempts.

I’m seeing threat intelligence reveal attackers targeting everything from 5G networks to remote workers. They’re launching multi-vector attacks that hit from all angles, and they’re particularly fond of exploiting those overlooked systems you might’ve forgotten about.

The rapid advancement of technology has left many organizations vulnerable, especially with end-of-life Windows 10 creating significant security risks for unprepared companies.

Essential Components of Effective Penetration Testing

After spending over a decade conducting penetration tests, I’ve learned that effective testing requires five essential components that work together like a well-oiled machine.

You’ll want to start by nailing down your test objectives and compliance requirements – trust me, I learned this the hard way after a few early fumbles. HIPAA compliance is especially critical when testing healthcare systems to protect sensitive patient data.

Next, immerse yourself in reconnaissance like you’re solving a puzzle, gathering every detail about your target. Financial fraud prevention has become a critical focus for institutions safeguarding customer assets.

Then move into vulnerability scanning, where you’ll uncover the weak spots. Selecting the right testing methodology framework will significantly enhance your vulnerability assessment effectiveness.

Follow up with controlled exploitation to prove what’s really at risk. Finally, wrap it all up with clear, actionable reporting that’ll drive real change.

Strategic Approaches to Customer Data Protection

Penetration testing might reveal vulnerabilities, but protecting customer data requires a thorough strategy I’ve found over my years in cybersecurity. You’ve got to think like a defender and an attacker simultaneously. I’ve found that managing the complete data lifecycle, from creation to disposal, forms your foundation.

I always start with strict access controls – they’re your first line of defense. With potential data breaches costing an average of $4.35 million, organizations can’t afford to take chances.

Then layer in encryption strategies for data both in motion and at rest. Implementing zero trust architecture has become essential for maintaining comprehensive security standards.

Add continuous monitoring to catch issues early, and regular risk assessments to stay ahead of threats. Organizations with mature response plans can save up to $2.66M in breach-related costs.

Trust me, this multi-layered approach keeps your customer data locked down tight.

Advanced Exploitation Techniques and Defense Mechanisms

Since discovering AI-powered threats in my network security practice, I’ve had to completely transform how I approach defense mechanisms.

What used to work against basic malware now fails against AI Malware that mutates in real-time. I’ve learned some hard lessons about staying ahead of these evolving threats. Continuous threat detection has become essential for identifying and neutralizing sophisticated attacks before they can cause damage.

  1. Deploy AI-powered monitoring systems that catch suspicious activity 24/7
  2. Implement zero-trust architecture to stop lateral movement dead in its tracks
  3. Use advanced authentication to prevent Deepfake Impersonation of executives
  4. Set up automated incident response systems that neutralize threats instantly

You’ve got to think like the attackers to protect your data. When they automate their attacks, we must automate our defenses even better. The rise of ransomware-as-a-service has made it easier than ever for criminals to launch devastating attacks against organizations.

Regular penetration testing has become crucial for validating security measures and staying ahead of emerging threats.

Building a Resilient Security Framework Through Testing

The countless hours I’ve spent battling AI-powered threats have taught me one unmistakable truth – we can’t just react to attacks anymore. You’ve got to build resilience into your security framework from day one, and I’ll show you how.

Start by integrating security testing frameworks throughout your development cycle, not just at the end. Our network penetration testing solutions identify vulnerabilities across your critical assets before malicious actors can exploit them.

Customer data protection remains paramount for maintaining trust and regulatory compliance in the automotive industry. I’ve learned this the hard way after countless sleepless nights patching vulnerabilities that could’ve been caught earlier. Implementing IAST runtime monitoring provides real-time insights into vulnerabilities as they emerge during testing phases.

Your security policies need to evolve with the threats, and testing must be continuous. Trust me, it’s better to find the weak spots yourself before the bad guys do.

Frequently Asked Questions

How Frequently Should Organizations Conduct Network Penetration Testing for Optimal Security Coverage?

You’ll want to conduct frequency analysis quarterly, but adjust testing intervals based on your risk level – monthly for high-risk sectors, annually for low-risk businesses, and immediately after major system changes.

What Certifications or Qualifications Should Professional Penetration Testers Possess?

Like a master locksmith, you’ll need core certifications including CEH or OSCP to prove your ethical hacking expertise. Don’t overlook CompTIA PenTest+ and GPEN – they’re your keys to professional penetration testing freedom.

How Do Cloud Environments Affect Penetration Testing Methodologies and Scope?

You’ll need to adapt your cloud security testing tools for shared infrastructure limits, dynamic asset discovery, and provider restrictions. Focus on IAM configurations and respect tenant boundaries while conducting automated and manual assessments.

Don’t bite off more than you can chew – you’ll need explicit written third party agreements and legal compliance documentation before testing others’ systems. Always get permission from every system owner to avoid criminal charges.

How Can Organizations Measure the Return on Investment From Penetration Testing?

You’ll maximize ROI by conducting thorough cost analysis of prevented breaches versus testing expenses, while your risk assessment data shows vulnerabilities found and fixed – directly measuring the value of your security investment.

Conclusion

You’re on the front lines of a constantly changing digital battlefield, where protecting customer data isn’t just a priority – it’s your mission. With over 20 years of experience, Firma IT Solutions stands as your trusted guardian in cybersecurity excellence. Our certified network penetration testing and ethical hacking services continuously adapt your defenses, test your fortress’s walls, and stay steps ahead of those who’d breach them. Backed by a 5.0 Google rating, our rigorous penetration testing and layered security strategies build an impenetrable shield that keeps your customers’ trust intact and their data secure. Call now for your initial assessment and fortify your digital defenses today.

CLICK HERE TO REQUEST A PENETRATION TEST QUOTE FOR SERVICE

ChatGPT Image Jun 8, 2026, 04_11_17 PM

The Hidden Cybersecurity Threat Lurking Inside Multi-Tenant Office Buildings

Shared Office Network Security: The Hidden Cybersecurity Threat Lurking Inside Multi-Tenant Office Buildings

Shared office network security is a growing concern for businesses operating in multi-tenant office buildings. Many companies assume they are protected because their computers work, the internet is fast, and the printer connects without issue. Unfortunately, those assumptions can create significant cybersecurity risks. When multiple businesses share the same network infrastructure without proper security controls, a cyberattack against one tenant can quickly become a cyberattack against everyone.

Across the country, countless office buildings house multiple businesses that share internet connections, networking equipment, and wireless infrastructure. In many cases, building owners provide internet access as an amenity, and tenants simply plug in and get to work.

However, many business owners never realize they may be sharing a network with every other company in the building.

Why One Compromised Computer Can Become Everyone’s Problem

Cybercriminals rarely stop at the first device they compromise.

Instead, once attackers gain access to a computer, they immediately search for other systems on the network. Security professionals call this process lateral movement. During this phase, attackers identify additional computers, servers, printers, network devices, and other connected systems.

Without proper network segmentation and security controls, attackers can potentially:

  • Access computers belonging to other tenants
  • Discover shared files and printers
  • Capture network traffic
  • Harvest usernames and passwords
  • Deploy ransomware across multiple organizations
  • Spread malware throughout the building
  • Disrupt operations for every tenant

As a result, a single employee clicking a malicious email attachment could trigger a cybersecurity incident that affects every company in the building.

“But We’re Not a Target”

Shared Office Network Security

This belief remains one of the most dangerous misconceptions in cybersecurity.

In reality, attackers do not care whether your company has five employees or five thousand employees. Modern cybercriminals use automated tools that continuously scan the internet for vulnerable systems.

Therefore, if your business shares an exposed network with other tenants, your security may only be as strong as the least secure company in the building.

For example, your organization may enforce strong passwords, multifactor authentication, endpoint protection, and security awareness training. Meanwhile, another tenant may operate outdated computers, weak passwords, or no cybersecurity protections at all.

When everyone shares the same network, everyone shares the same risk.

The Liability Question for Building Owners

Building owners and property managers should pay close attention to this issue.

Although liability varies by jurisdiction and contractual agreements, providing internet service without proper network segmentation can create significant legal and financial exposure.

Following a cyber incident, investigators, attorneys, insurance carriers, and affected tenants may ask important questions:

  • Did the building owner implement reasonable security measures?
  • Were tenants informed they shared a network with other businesses?
  • Was network segmentation available but never deployed?
  • Were known cybersecurity risks ignored?
  • Was the network represented as secure when it was not?

Furthermore, if ransomware spreads from one tenant to another because every business operates on the same unrestricted network, investigators will closely examine how the network was designed and managed.

Ultimately, the cost of implementing proper cybersecurity controls is often insignificant compared to the financial, operational, and legal consequences of a major breach.

The Hidden Risk of Sharing a Network with Other Businesses

Shared Office Network Security

Many tenants have no idea they are exposed.

Most business owners focus on serving customers, generating revenue, and managing daily operations. Consequently, they often assume that if the internet works and systems connect properly, everything must be secure.

Unfortunately, functionality and security are not the same thing.

A business may unknowingly share network space with:

  • Insurance agencies
  • Healthcare providers
  • Law firms
  • Financial services companies
  • Collection agencies
  • Retail businesses
  • Contractors
  • Professional service firms

Each organization brings a different level of cybersecurity maturity and risk.

As a result, one compromised system can become a bridge into every other organization connected to the same network.

What Proper Shared Office Network Security Should Look Like

A properly designed business network separates each tenant from every other tenant.

Cybersecurity professionals typically accomplish this through:

  • VLAN segmentation
  • Firewall isolation
  • Network access controls
  • Secure wireless architecture
  • Traffic filtering and monitoring
  • Separate guest and business networks

These controls create barriers between organizations and significantly reduce the likelihood of a compromise spreading across multiple businesses.

Think of it this way: if a fire starts in one apartment, firewalls and barriers help prevent the entire building from burning down.

The same principle applies to cybersecurity.

Why Network Segmentation Matters

Network segmentation serves as one of the most effective defenses in a multi-tenant environment.

Without segmentation, every device on the network may be able to communicate with every other device. Consequently, attackers can move freely between systems once they gain an initial foothold.

With proper segmentation, however, each tenant operates within its own protected environment. Even if one organization experiences a cybersecurity incident, attackers face significant barriers when attempting to reach neighboring businesses.

For this reason, network segmentation should be considered a fundamental component of office building cybersecurity.

Businesses Still Need Their Own Security

Even when a building provides a secure network, each tenant must still protect its own environment.

Therefore, every organization should implement:

  • Endpoint protection
  • Multi-factor authentication
  • Security awareness training
  • Vulnerability management
  • Regular backups
  • Network monitoring
  • Penetration testing

Most importantly, building security and tenant security must work together as layered defenses.

Neither one alone provides sufficient protection.

Don’t Assume Your Shared Office Network Security Is Adequate

If your office is located in a multi-tenant building and you are unsure how the network is configured, now is the time to ask questions.

Ask your building owner or property manager:

  • Who manages the network?
  • Are tenants separated from one another?
  • Can devices belonging to other businesses communicate with our systems?
  • Has the network undergone a network security assessment?
  • What controls protect tenants from each other?

If you do not know the answers, your business may be carrying far more risk than you realize.

At Firma IT Solutions, we help organizations identify hidden weaknesses through network security assessments, penetration testing, and cybersecurity consulting. Before a cybercriminal discovers a weakness in your environment, make sure a trusted cybersecurity professional finds it first.

Contact Firma IT Solutions today at 303-209-0386 to learn how we can help keep your business connected and protected.

CLICK HERE TO REQUEST A PENETRATION TEST QUOTE FOR SERVICE